Application Security Review
We test your web and mobile app against the OWASP Top 10: authentication, access control, injections, data exposure, so you know where an attacker would get in.
We review your code, infrastructure and data flows for vulnerabilities, then hand you a prioritized fix plan before attackers, investors or auditors find them.
We test your web and mobile app against the OWASP Top 10: authentication, access control, injections, data exposure, so you know where an attacker would get in.
A senior engineer reads the code for vulnerabilities, hardcoded secrets, unsafe dependencies and risky patterns, including code written by AI tools.
We check your AWS, GCP or Azure setup: IAM roles, network exposure, storage permissions, backups and logging, so a single misconfiguration doesn't leak everything.
We trace where personal and payment data lives and moves, and check encryption, retention and access against GDPR or HIPAA expectations.
We turn every finding into a prioritized fix list with effort estimates, so you know what to close this week and what can wait.
Each finding rated critical, high, medium or low.
Steps to reproduce and evidence, not scanner noise.
Where your data, users and business are exposed.
A summary for investors, clients or compliance teams.
Scope, effort and order of fixes, ready for a decision.
We verify that critical issues are actually closed.
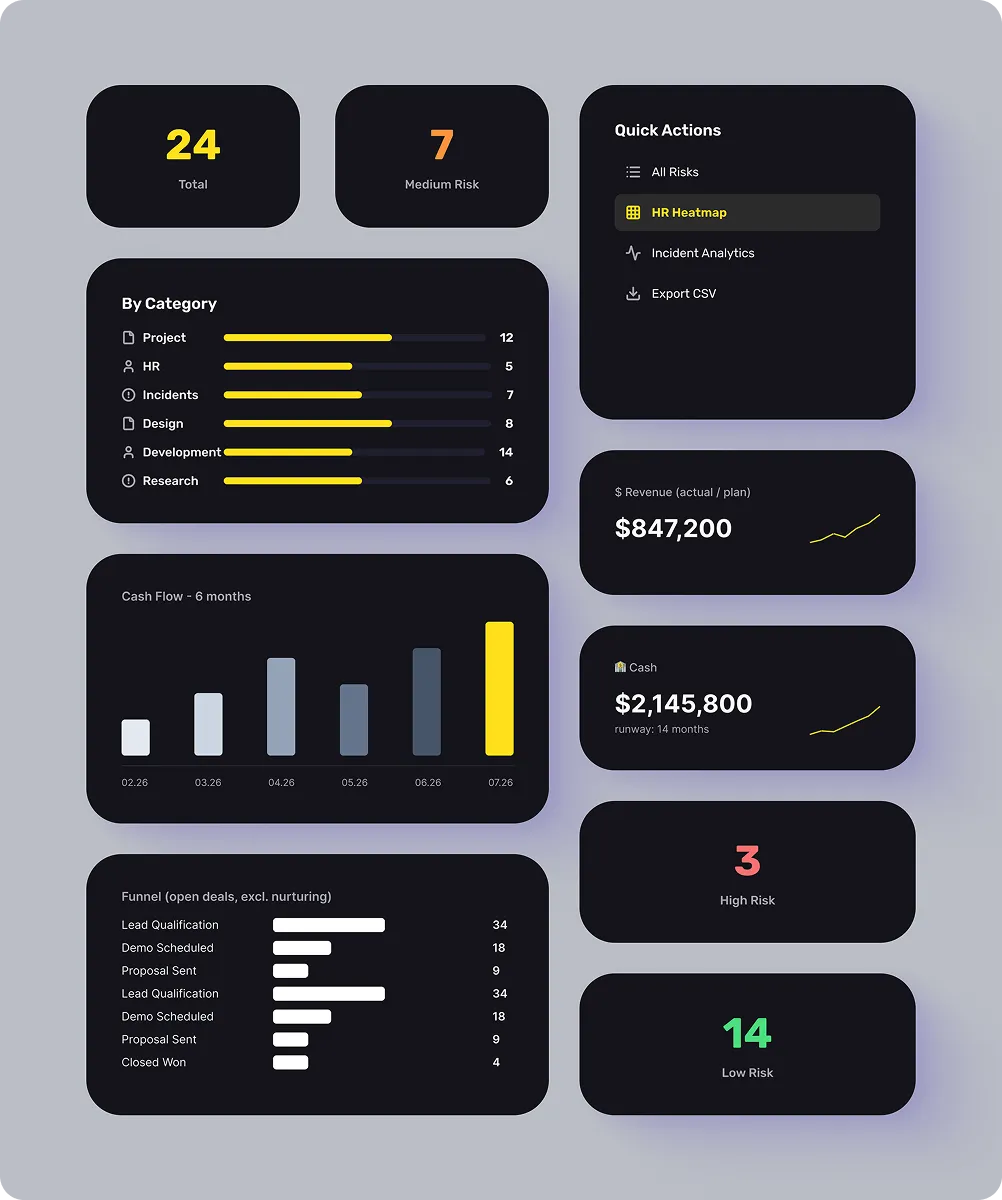
Fix now, monitor, or schedule the next audit.
Fast enough to answer a client questionnaire or close a funding round on time.
A recognised standard your clients and auditors already understand.
Every issue is confirmed manually, so your team never chases false positives.


Quick Security Audit · €2,000
A fixed-price check of your app, code and cloud setup by a senior engineer. You get the critical risks, evidence and a fix plan in days, not weeks.
Fixed price. No obligation to order a full audit.
Enough products seen up close to know what breaks and why.
Every audit is done by a senior engineer, not a junior with a scanner.
Clients value the honesty of our findings as much as the fixes.
We know how to read and secure code nobody documented.
Kyle's unstable app, diagnosed and fixed after its vendor shut down.
Spread's outdated codebase, audited and rebuilt on React Native.
Which apps, environments and data are in scope?
NDA first, then read-only access to code and cloud.
Automated scans plus manual review and testing.
Every finding with severity, evidence and a fix.
We verify the critical fixes. Your call on the rest.
We’ll assess your system, process, or data challenge and recommend the most practical next step.
No sales pressure. You’ll speak with a specialist who can actually assess the project.

Consult an expert, not a script.

If needed, we’ll sign an NDA first

We'll assess your situation first.

Get practical steps, not a generic pitch.
The Quick Security Audit costs a fixed €2,000 and covers the most critical risks in your app, code and cloud setup. A full audit depends on the scope: one web app, a mobile app with its API, or a full product with its infrastructure. We agree a fixed price before we start.
A focused audit of one application usually takes 5 to 10 working days. Larger scopes with several apps and cloud environments take longer; we give you the timeline upfront.
It includes penetration-style testing of your application, combined with code and configuration review. That mix finds more than a black-box test alone, because we see both how the product behaves and why.
No. We test on staging where possible, and any testing against production is agreed in advance, rate-limited and scheduled at a time that suits you.
Read-only access to the repository and cloud accounts, plus test accounts in the app. We sign an NDA first, never copy production data, and remove our access when the audit ends.
An audit is not a certification, but it covers the technical controls those frameworks expect and gives you a report to share with auditors, clients or investors.
Yes. Independent review of a previous vendor's or AI-generated code is one of the most common reasons teams come to us.
Yes, if you want us to. The report comes with a fixing estimate, but there's no obligation. You can hand it to any team you choose.